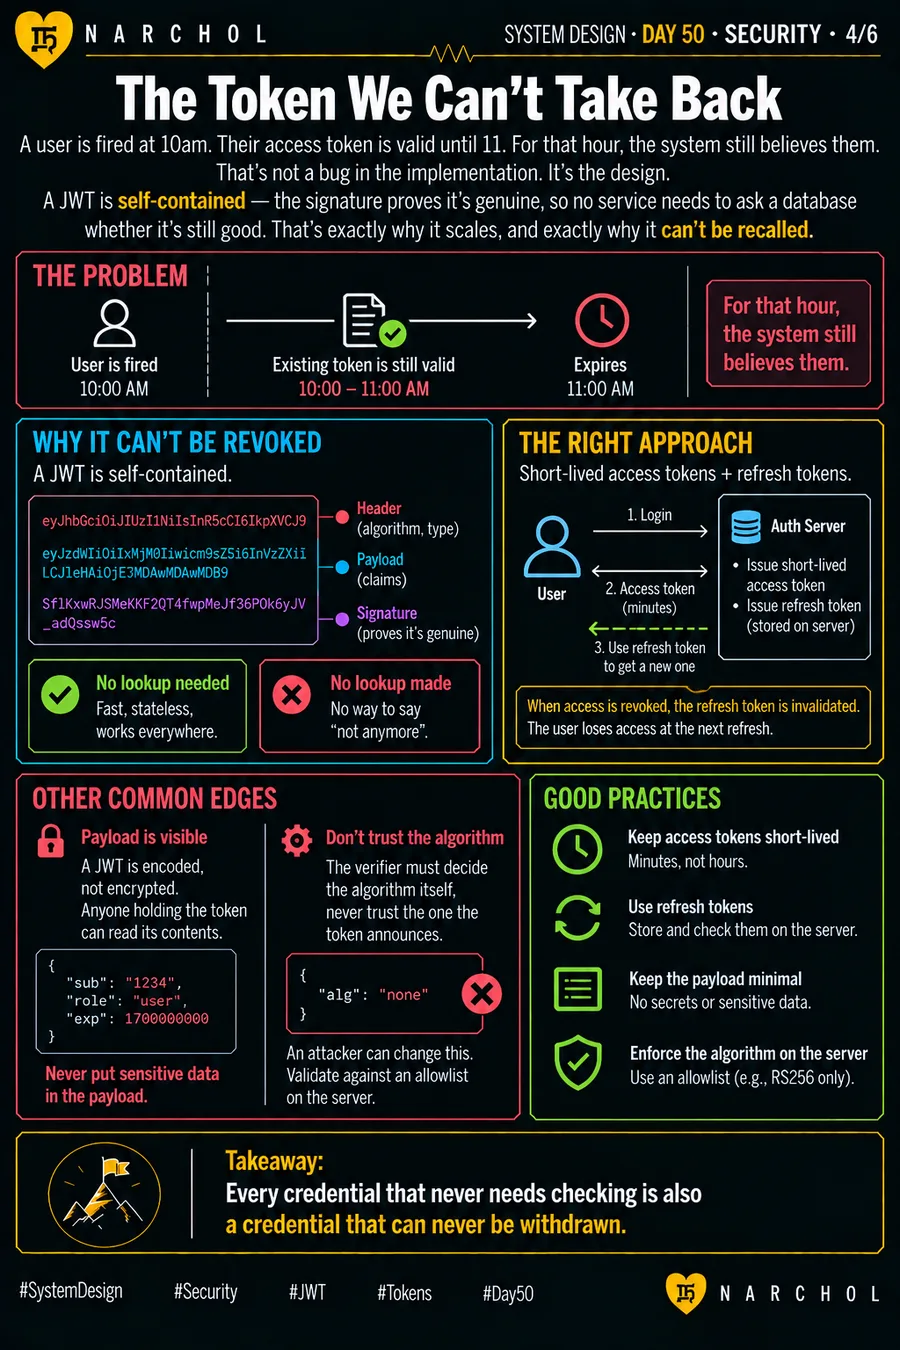
A user is fired at 10am. Their access token is valid until 11. For that hour the system still believes them, and no amount of shouting at the code will change it, because the behaviour was chosen rather than introduced.
A JWT is self-contained. The signature proves it is genuine, so no service has to ask a database whether it still ought to be honoured. That property is exactly why it scales across dozens of services, and exactly why there is nowhere to go to say "not anymore".
The practical answer is to shorten the window. Access tokens live for minutes, a refresh token lives on the server where it can be deleted, and revoking access means invalidating the refresh token so the user drops out at the next renewal.
Two smaller edges catch people. The payload is encoded rather than encrypted, so anyone holding the token can read it. And the verifier must decide the algorithm itself, against an allowlist — a token announcing "alg": "none" is a question, never an instruction.
Every credential that never needs checking is also a credential that can never be withdrawn.