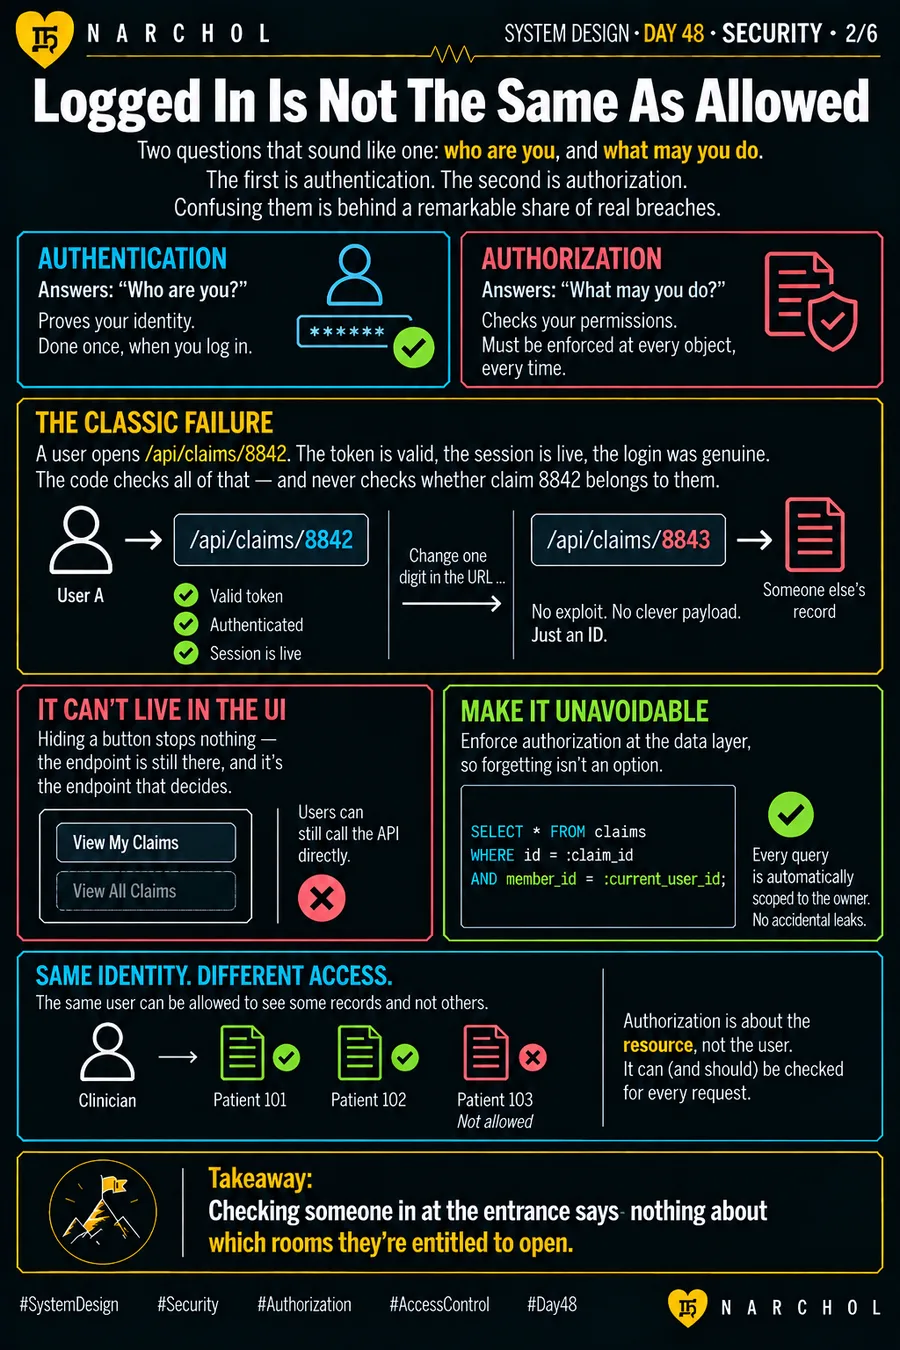
Two questions that sound like one: who are you, and what may you do. The first is authentication and happens once, at login. The second is authorization and has to be enforced at every object, every time. Confusing them sits behind a remarkable share of real breaches.
The classic failure looks like nothing. A user opens /api/claims/8842. The token is valid, the session is live, the login was genuine. The code checks all of that and never checks whether claim 8842 belongs to them. Change one digit in the URL and you are reading someone else's record. No exploit, no clever payload — just an ID.
It can't live in the interface either. Hiding a button stops nothing, because the endpoint is still there and it is the endpoint that decides. The durable fix is at the data layer, where every query is scoped to the owner and forgetting stops being an option.
Checking someone in at the entrance says nothing about which rooms they're entitled to open.